pcapLume
Local PCAP forensics for macOS.
Reads Ethernet .pcap and .pcapng captures on your Mac, carves files from unencrypted HTTP downloads, and, with Pro, writes PDF reports that print the capture file’s hashes and state what was read and what was not. Your capture file is never uploaded.
The capture file’s MD5, SHA-1 and SHA-256 appear on the dashboard and in the Integrity Record (Pro), which also records how the file was read and what was analyzed. The record states that it is not a chain of custody.
A separate hash-chained log. Recording entries is free; the printed log is Pro. Each entry is marked observed by the software or asserted by a person, and verification names the entry where the chain first breaks, whether altered, removed or reordered. It uses no secret, so it does not hold against someone with full write access to your Mac.
Rebuilds JPEG, PDF, ZIP, EXE and HTML files downloaded over unencrypted HTTP and records a SHA-256 for each complete file. Incomplete files are marked as such. Carved files, and in-app image and PDF previews, are Pro.
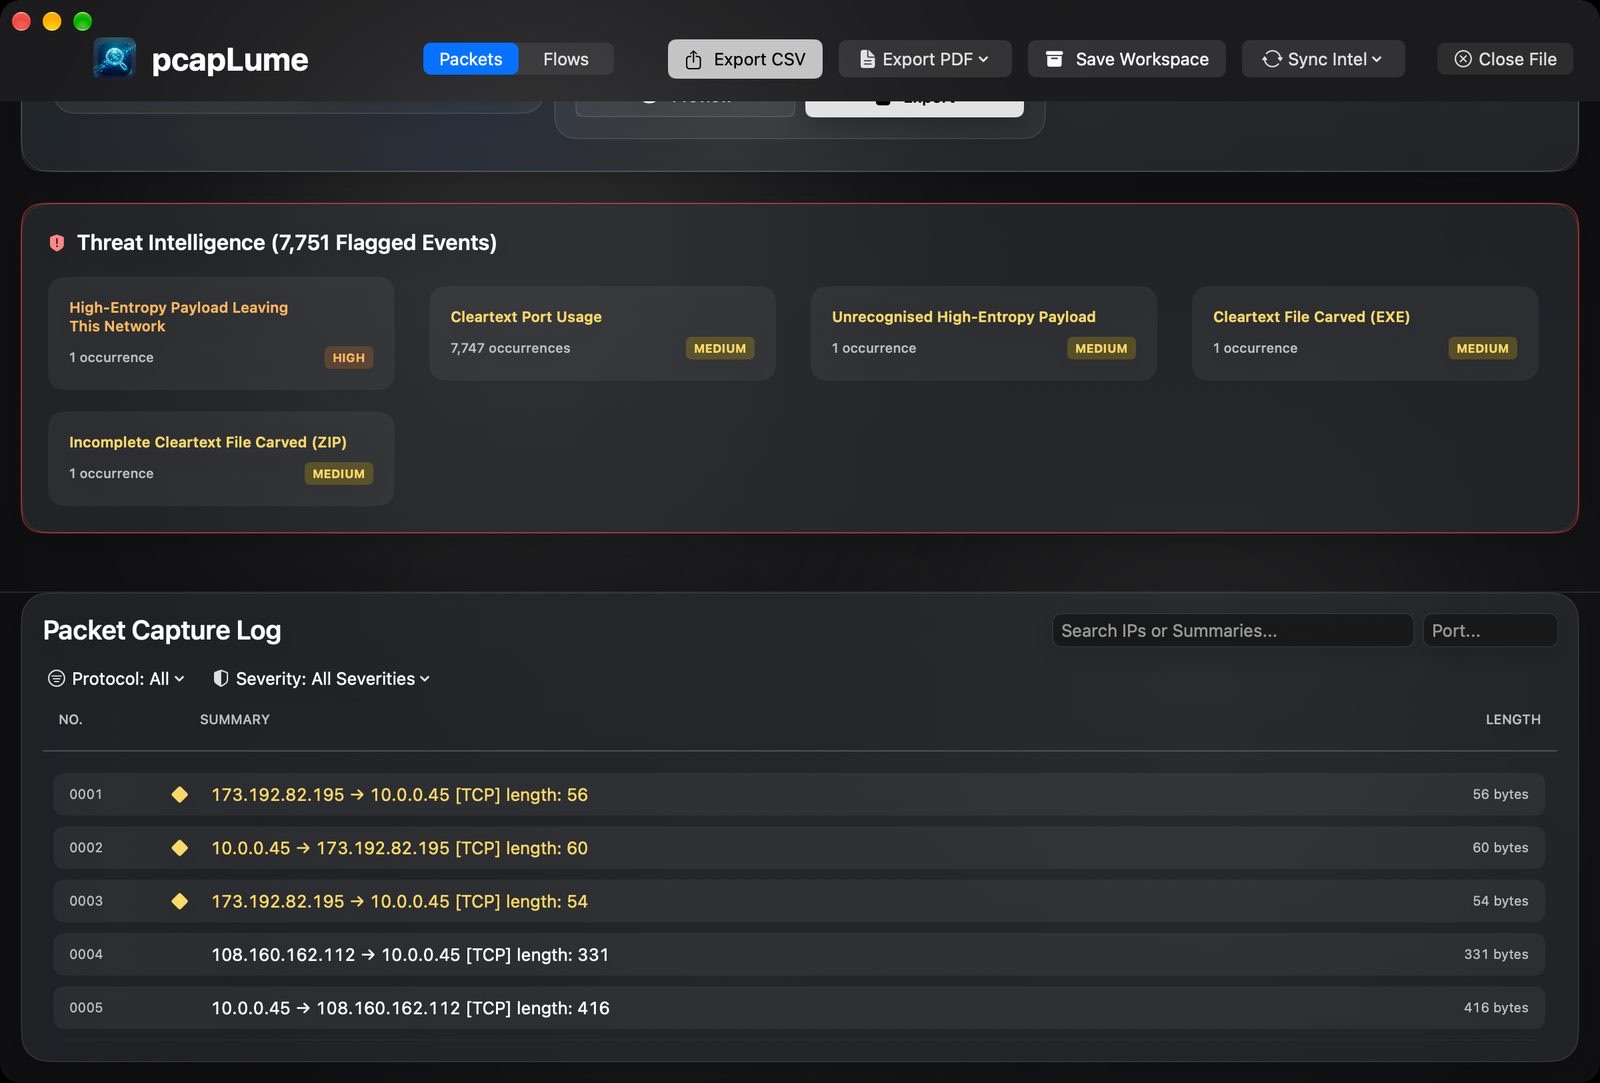
Flags beacon-like traffic when the last 15 packets of a flow arrive at near-constant intervals (variation under 5%, average gap over one second), payloads with high Shannon entropy, and five fixed built-in payload signatures. There is no rule language and the signatures cannot be edited; you can import your own indicator lists.
Finds credentials, emails, phone numbers, URLs, US Social Security numbers and payment card numbers that pass a Luhn check and carry a recognised issuer prefix, in cleartext on TCP ports 80, 21 and 23. TLS is never decrypted.
Shows each packet’s main header fields (MAC addresses, EtherType, IPv4 addresses, protocol, ports, HTTP host, DNS queries) and its decoded payload, with protocol, port and severity filters and search. Free shows the first 25 packets and flows, and Pro shows all of them. It reads Ethernet II captures only and up to 1,000,000 packets. Only IPv4 is decoded; IPv6 and VLAN-tagged frames are counted, not decoded.
Zero Telemetry is a switch. It is off unless you turn it on, in Guided Setup or in Settings, and Simple Setup leaves it off. While it is off, two lookups run without a click: with Pro, geojs.io receives the public addresses in Top Talkers; and if you have saved your own abuse.ch key, MalwareBazaar receives the SHA-256 of files carved from a capture (abuse.ch can link each hash to that account). With no key saved, nothing goes to MalwareBazaar. The rest run only when you ask: with Pro, Shodan and Censys look up an address you pick, using your own keys (if you choose “Send for the Rest of This Session”, each packet you select afterwards is looked up without asking again, until you stop it or quit), the Test buttons in Settings check your saved keys with Shodan, Censys and abuse.ch, and AlienVault OTX (your own key), the abuse.ch feeds and the IEEE vendor list download when you press Sync. With Zero Telemetry on, pcapLume makes no outside call of its own. Two things happen whether it is on or off: Apple’s StoreKit reaches the App Store for prices and licenses, and an IP address shown as a link opens whois.domaintools.com in your browser when you click it. Links to profworkbench.com and auth.abuse.ch open in your browser. The capture file itself is never uploaded, and the app does not contact ProfWorkBench. Settings names every host and what triggers it.
Free opens a capture and runs the whole analysis, shows findings as counts, and lists the first 25 packets and flows. Pro adds all seven PDF reports, CSV export, threat details, carved files, the full packet and flow lists, the locked Intelligence Dashboard panels, and Shodan, Censys and geolocation enrichment. Pro (Annual) renews automatically, and there is no trial.
US prices; other regions vary. Educational, military, and first-responder discounts apply; see Academic & Service Discounts.